New Index Engines Research Finds Ransomware Variants Built to Evade Detection and Undermine Recovery
HOLMDEL, N.J., Sept. 30, 2026
Press Release Disclaimer: This is a press release distributed through the XPR Media network. It has not been independently verified by our newsroom.

New Index Engines Research Finds Ransomware Variants Built to Evade Detection and Undermine Recovery
PR Newswire
HOLMDEL, N.J., Sept. 30, 2026
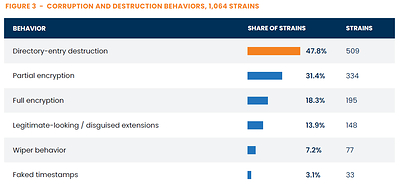
The CyberSense Research Lab analysis of 1,064 ransomware strains finds directory destruction in more than twice as many variants as full encryption
HOLMDEL, N.J., Sept. 30, 2026 /PRNewswire/ — Index Engines the leader in cyber resilience, today announced its latest findings from its proprietary CyberSense® Research Lab (Patent #12248574) revealing a shift in ransomware behavior, with a growing share of analyzed variants using corruption techniques that avoid the traditional signs of obfuscation.
Among 1,064 ransomware strains acquired and detonated during the first half of 2026, 47.8% exhibited directory-entry destruction, more than twice the 18.3% that exhibited full encryption. The lab also documented new ransomware designed to suppress familiar signs of corruption by preserving file extensions and timestamps, maintaining low entropy, encrypting slowly, and targeting only selected sections of files.
“Bad actors know what scanning tools look for, and the variants we detonated this year are built to hide it,” said Jim McGann, CMO of Index Engines. “Encoder is the clearest example. It destroyed files while leaving their names, sizes, timestamps, and entropy unchanged. A surface scan would report that data as clean. CyberSense caught it by analyzing the content and structure of each file. The Research Lab exists to find techniques like this early and build them into the model our customers rely on for recovery.”
The CyberSense Research Lab automates the ingestion and behavioral analysis of ransomware variants in a controlled environment, enabling continuous training of AI/ML models on real-world attack patterns and, enabling continuous training of AI/ML models on real ransomware behavior. The result is more comprehensive corruption detection that keeps pace with the threat landscape, backed by 99.99% ESG-validated accuracy, and smarter recovery decisions for organizations facing today’s cyber criminals.
Key findings* from the H1 2026 research include:
- Ransomware is moving beyond full encryption: Directory-entry destruction was the most common behavior identified by the Lab, appearing in 47.8% of strains analyzed.
- Traditional signs of corruption are disappearing: Variants suppressed traditional signs of corruption including changed extensions, entropy spikes, altered timestamps and rapid file changes.
- The window to respond is shrinking: Lab detonations showed a median attack velocity of approximately 97,321 files corrupted per hour, reaching 10,000 files in about six minutes.
- AI is not present at the point of impact: None of the 1,064 strains showed AI making choices about data at the destructive payload stage. Industry research from Palo Alto Networks and ReliaQuest places AI’s current footprint earlier in the attack lifecycle, where it is compressing reconnaissance and lateral movement.
- The findings change the recovery equation: As ransomware moves beyond encryption and suppresses traditional signs of corruption, data that appears unaffected may not actually be clean. Organizations need to validate the integrity of their data before trusting it for recovery.
The research also found polymorphism at work in 64.7% of analyzed samples. These variants kept their functional code intact while regenerating their file signature between builds, so each new infection presented a fingerprint that signature-based tools have never previously seen.
At the data layer, the Lab documented variants that used partial encryption, preserved or faked timestamps and low-entropy corruption to shrink the visible footprint of an attack. These techniques evade detection that depends on entropy spikes or bursts of encryption activity.
“In our detonations, ransomware reached 10,000 files in about six minutes, which is faster than most Incident Response escalation paths,” McGann added. “By the time a team moves to recovery, the question is which copy of the data can be trusted. CyberSense answers it with a forensic account of what was affected and pinpoints clean data to restore from.”
Access the full CyberSense Research Lab report at www.indexengines.com
* Findings reflect variants acquired and detonated by the CyberSense Research Lab and are not an estimate of how often each technique appears in real-world attacks. Individual samples can exhibit multiple behaviors, so percentages reflect overlapping patterns.
About Index Engines
At Index Engines, we are experts in Cyber Resiliency, helping organizations build an infrastructure where trusted data is available and reliable. Our leading solution, CyberSense, provides a 99.99% SLA for detecting ransomware corruption. CyberSense empowers organizations to confidently navigate cyber challenges, mitigate risks, and quickly recover to normal business operations in the ever-evolving cyber landscape. For more information, visit www.indexengines.com.
 View original content to download multimedia:https://www.prnewswire.com/news-releases/new-index-engines-research-finds-ransomware-variants-built-to-evade-detection-and-undermine-recovery-302892614.html
SOURCE Index Engines